Skip to content

Code signing and cryptographic governance for vehicle and machine manufacturers.

KT Secure runs sovereign, multi-supplier code signing for cars, buses, trucks and off-highway machines. Signing keys stay in UK-hosted hardware under one policy. You get the evidence UN R155 and R156 ask of road vehicles, the evidence the EU Machinery Regulation asks of machines, and a planned route to post-quantum signatures.

Brief our team

A vehicle built in 2026: 15-year service life

Classical signatures (RSA, ECDSA)

Classical signature algorithms such as RSA and ECDSA are permitted until 2030, phased out until 2035 and disallowed after that. A vehicle built in 2026 has a service life running to 2041.

The gap: A vehicle built in 2026 can still be receiving signed updates six years after classical signatures are disallowed.
20+
Multi-supplier, HSM-backed signing estates
Level 3
Signing keys held in FIPS 140-3 validated HSMs, hosted in the UK
ISO27001 and 22301
Information security and business continuity, both certified by BSI

Who we serve

For manufacturers with many software suppliers and a regulator to answer to

We fit where three things meet: a dated regulatory duty on your software, code arriving from many suppliers, and a need to keep signing keys under your own control.

Brief our team
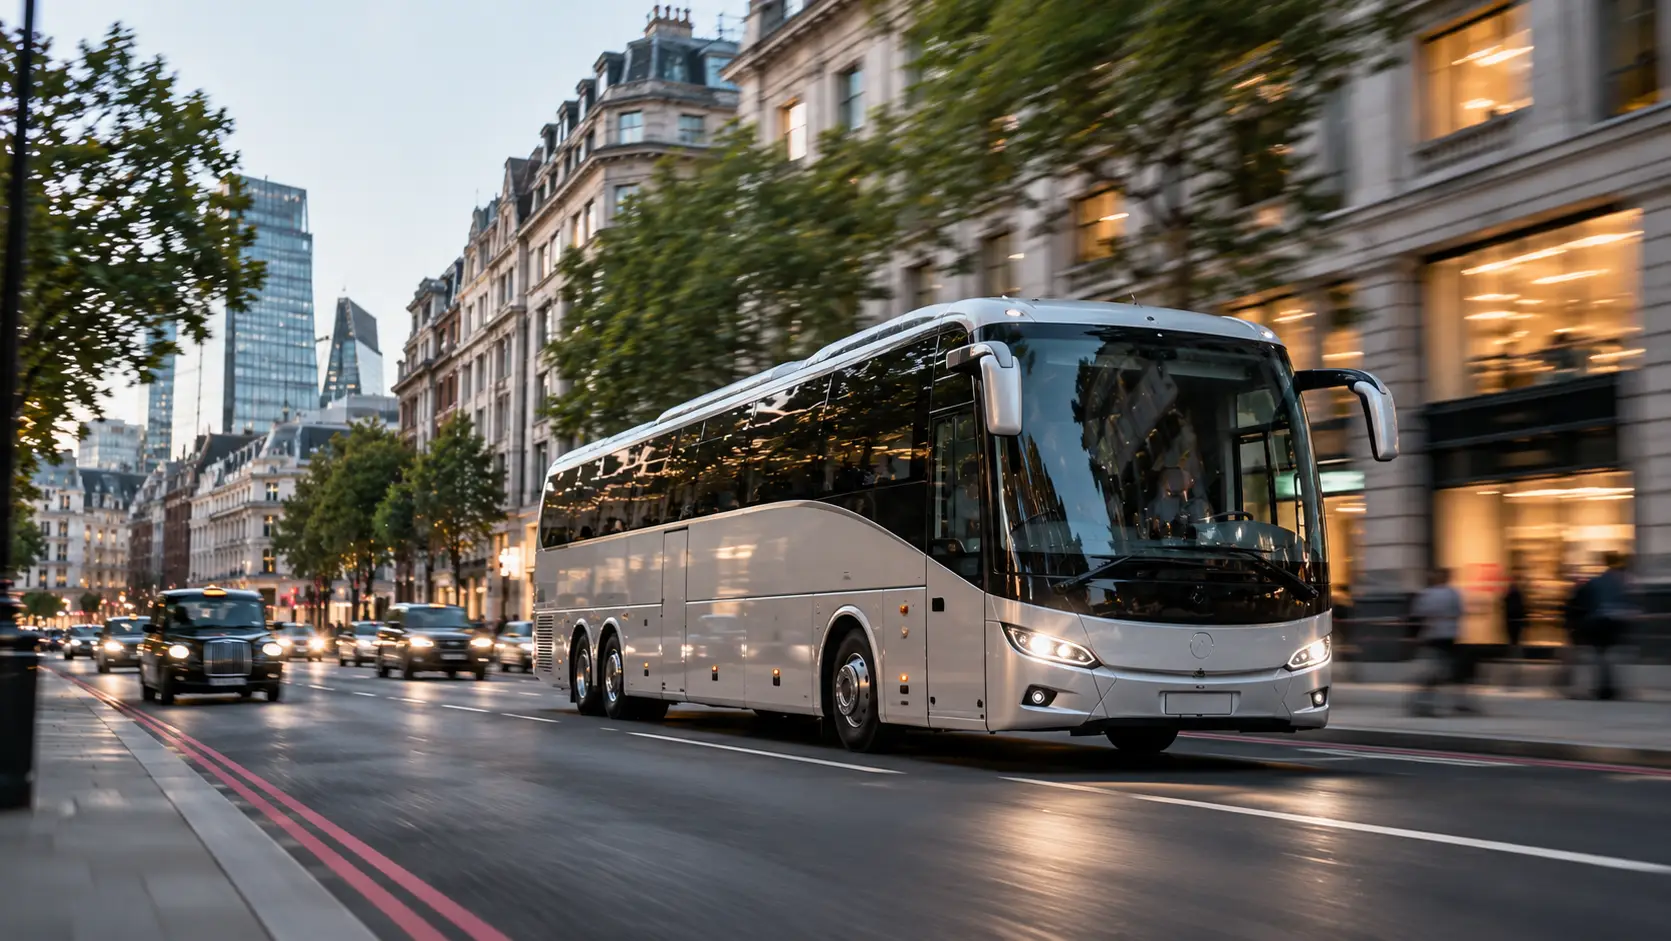
  • Coach on a London street, representing commercial vehicle manufacturers

    Commercial vehicle
    manufacturers

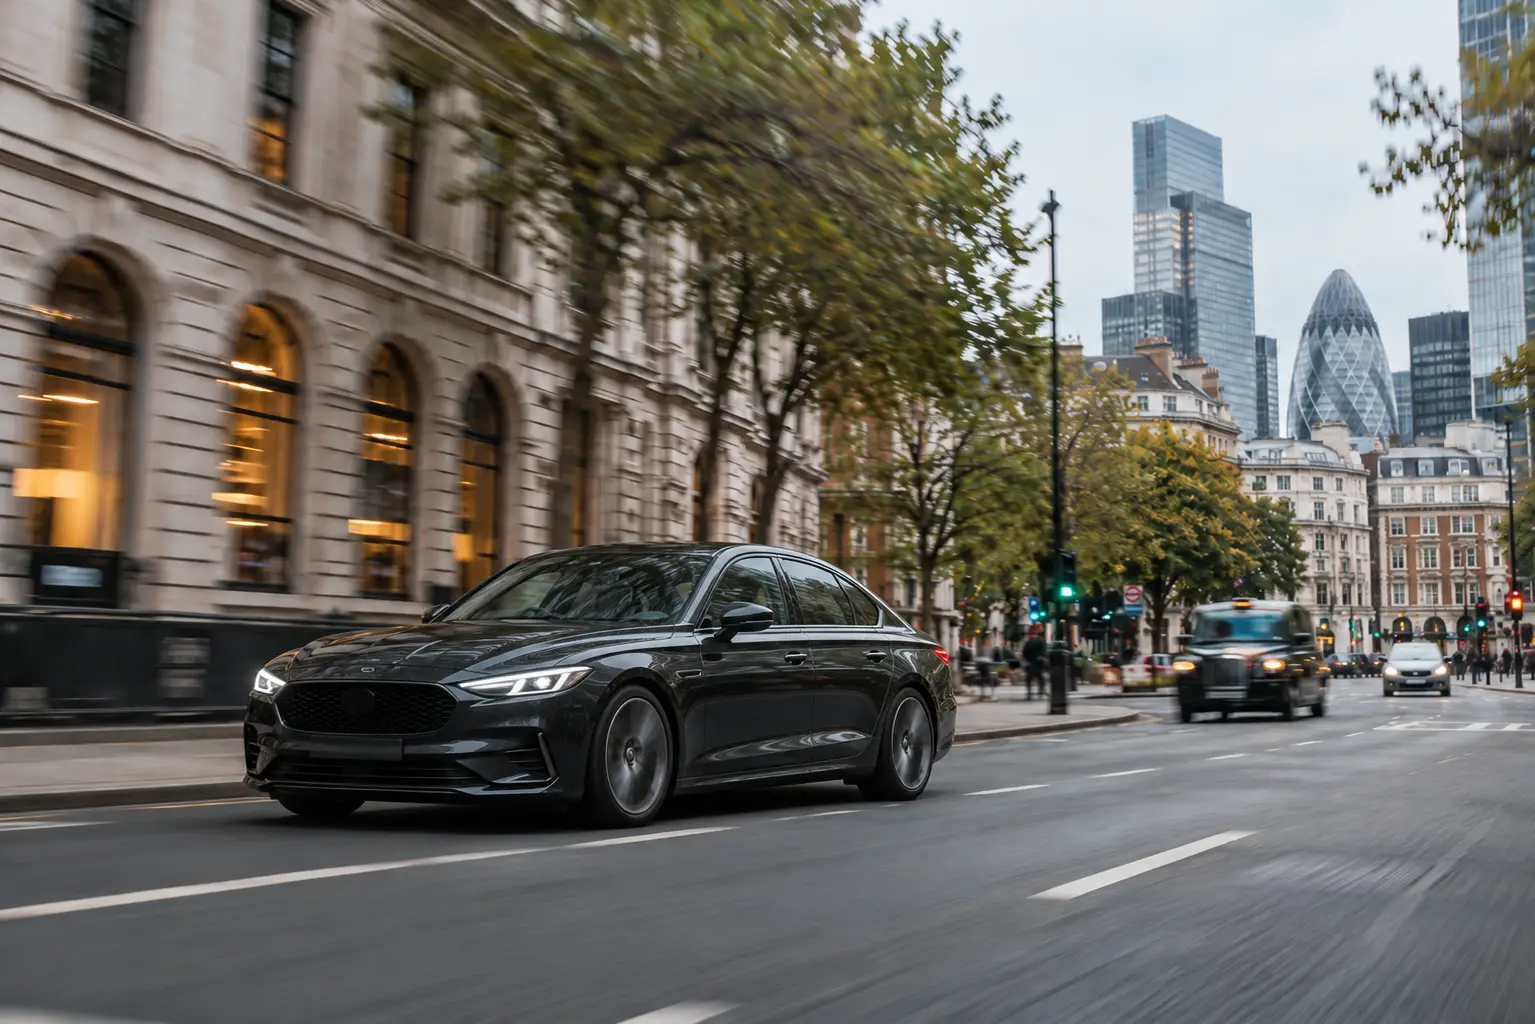
  • Premium saloon car on a city street, representing premium vehicle manufacturers

    Premium vehicle
    manufacturers

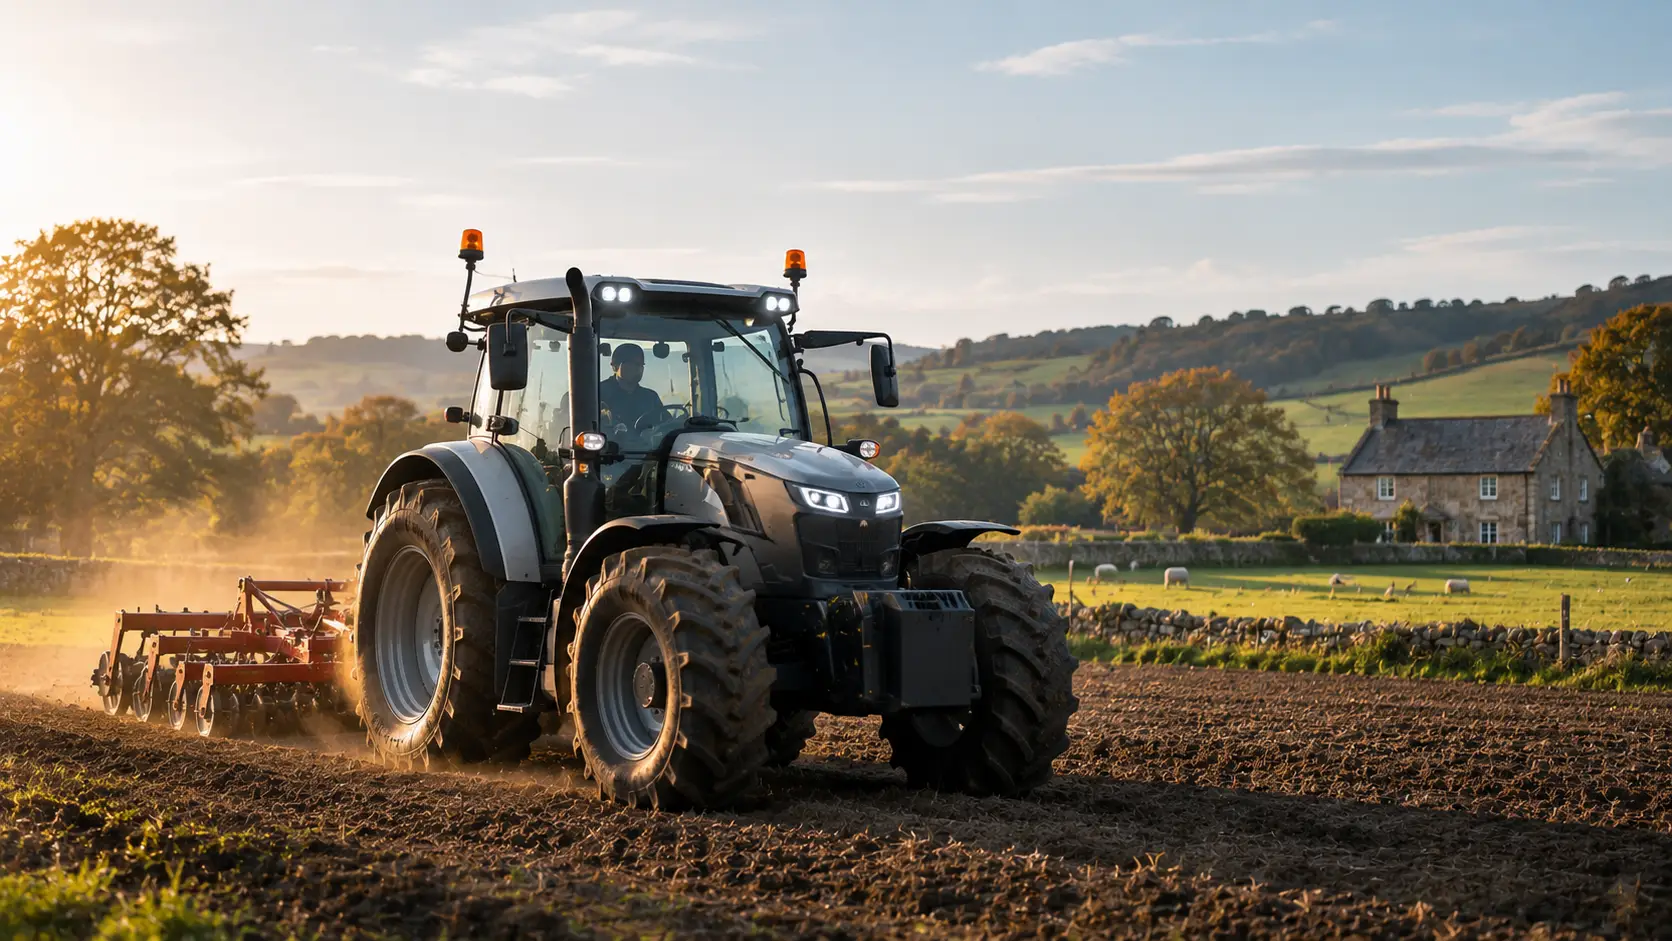
  • Tractor working a field, representing off-highway and agricultural machine manufacturers

    Off-highway and agricultural
    machine manufacturers

  • UN R155
  • UN R156
  • ISO/SAE 21434
  • EU Machinery Regulation

We also work in the Gulf region through partners.

Two service lines.
One accountable team.

Service line

The Infrastructure Layer

Service line 01: Cryptographic infrastructure

One signing service. Many signing types running at once.
On a sovereign estate.

Flagship

Multi-supplier code signing

OTA firmware, applications, CI/CD pipelines, certificate issuance and electronic certificates of conformity, all on one sovereign estate. Built for manufacturers with code arriving from many suppliers, whether that is three or thirty.

Brief our team
  • HSM management
  • PKI design and governance
  • Certificate lifecycle
  • Supplier onboarding

Service line

The Governance Layer

Service line 02: Cryptographic visibility and governance

Policy, evidence and a clear view of your post-quantum
exposure, from practitioners who have run it.

Flagship

CBOM scan

An inventory of every algorithm, key and certificate a product relies on, showing where quantum-vulnerable cryptography sits and how exposed you are.

Brief our team
  • Cryptographic policy
  • Regulatory evidence
  • Post-quantum readiness

Certified where it counts.
Fluent in the mandates that matter.

Our own management systems are certified by BSI. The standards below are the frameworks your approval authority and auditors work from. The people who design your environment are the people who operate it.

Brief our team

Held by KT Secure

  • ISO/IEC 27001:2022
  • ISO 22301:2019

Both certified by BSI.

Standards we work to

  • UN R155
  • UN R156
  • ISO/SAE 21434
  • NIS2
  • EU Post-Quantum Roadmap
  • EU Machinery Regulation

Signing keys sit in FIPS 140-3 Level 3 validated hardware security modules. The validation belongs to the hardware, not to KT Secure.